TAC Bridge Incident
Incident Summary#
On May 11, 2026, the attacker sent forged deposit notifications from counterfeit Jetton Wallets. TAC’s sequencers accepted them and authorized the minting of unbacked USD₮, BLUM, and tsTON. The attacker then withdrew genuine tokens from TON custody, causing approximately $2.85M in losses.12
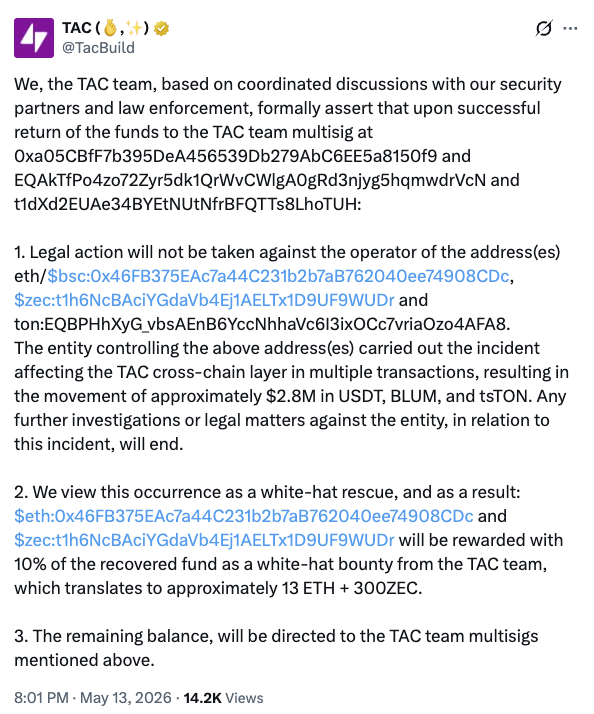
TAC negotiated the return of funds in exchange for a 10% bounty (~13 ETH + 300 ZEC) and a promise not to pursue legal action once the funds were returned. TAC treated the incident as a “white-hat rescue.”3
On May 14, the attacker began transferring assets to TAC-controlled multisigs and handed over a wallet’s private key.4 TAC’s May 20 report recorded $2.29M in recovered funds (80.2% of the reported loss).
Background#
What are TON and TAC?#
- TON (The Open Network): A Layer 1 blockchain using the TON Virtual Machine (TVM).5
- TAC: A separate EVM-compatible Layer 1 blockchain connected to TON through the TON Adapter, which handles cross-chain messages and asset transfers.6
What are USD₮, BLUM, and tsTON?#
| Token | Description | Incident impact |
|---|---|---|
| USD₮ | Tether’s USD stablecoin, designed to maintain a value of approximately USD 1. It has a canonical Jetton Master on TON. | Loss: 2,434,872.769394 USD₮. USD₮ accounted for the largest loss because the bridge held substantial genuine USD₮ reserves.2 |
| BLUM | Utility token of the Telegram-native Blum ecosystem. BLUM is not a stablecoin and its price fluctuates. It is available on TON, TAC, BNB Chain, and other networks.7 | Actual loss: 117,414,348.59482776 BLUM. |
| tsTON | Tonstakers’ liquid staking token (LST), representing a claim on staked TON and staking rewards. Its value in TON rises as rewards accrue.8 | Approximately 25,751.5 unbacked tsTON were minted on TAC. Insufficient reserves on TON limited the actual theft to 8,277 tsTON. |
ERC-20 and TEP-74#
- ERC-20: The fungible-token standard used on TAC. The token contract tracks balances by owner address.9
- TEP-74 (Jettons): TON's fungible-token standard. Each token has a Jetton Master and a separate Jetton Wallet contract for each owner, holding that owner's balance.10
- Bridge flow: TON → TAC locks Jettons and mints corresponding ERC-20 tokens; TAC → TON burns those tokens and releases the locked Jettons.
Normal Bridge Flow and Missing Validation#
Unable to render diagram.
Sources: 11; bridge execution1213; missing checks1.
Attack Flow#
| Chain | Entity | Address |
|---|---|---|
| TON | Attacker TON Wallet | EQBPHhXyG_vbsAEnB6YccNhhaVc6I3ixOCc7vriaOzo4AFA8 |
| TON | Counterfeit Jetton Wallet(s) | Example: EQA8rR5ofiIdpOO7l1JNSE0dthUp1AOxw0T5tO7ONIOkv9e9 |
| TON | Counterfeit Jetton Wallet in referenced Step-2 trace | EQAji_VNPbAdesJg1MDIXbcmD43hNfmwYi73yff48VNoX64z |
| TON | TAC Jetton Proxy | EQAChAswsPNsU2k3A5ZDO_cfhWknCGS6WMG2Jz15USMwxMdw |
| TON | TON Cross Chain Layer | EQAgpWmO8nBUrmfOOldIEmRkLEwV-IIfVAlJsphYswnuL80R |
| TON | Settings | EQBpUijPLYC9dcmw8Y-d23E9iX-2HBCupc5oqoYgXnORSRmi |
| TON | Canonical USD₮ Jetton Master | EQCxE6mUtQJKFnGfaROTKOt1lZbDiiX1kCixRv7Nw2Id_sDs |
| TON | Canonical BLUM Jetton Master | EQCAj5oiRRrXokYsg_B-e0KG9xMwh5upr5I8HQzErm0_BLUM |
| TON | Canonical tsTON Jetton Master | EQC98_qAmNEptUtPc7W6xdHh_ZHrBUFpw5Ft_IzNU20QAJav |
| TON | JettonProxy-owned custody Jetton Wallets | Separate address for each token |
| TON | Attacker-owned genuine Jetton Wallets | Separate address for each token |
| TAC | TAC Cross Chain Layer | 0x9fee01e948353E0897968A3ea955815aaA49f58d |
| TAC | Consensus | 0xAe635dE674cFE4aFD179CDE441aBBE6504A20A98 |
| TAC | USD₮ representation | 0xAF988C3f7CB2AceAbB15f96b19388a259b6C438f |
| TAC | tsTON representation | 0xD44F691aeD69fe43180B95b6F82f89c18Fb93094 |
| TAC | BLUM | 0x659CAbE7D88541f045faBD81c87F0f4B1510196C |
| TAC | BlumAdapterUpgradeable | 0xfDc8Cd47848c0C67dF66F7120F4e3371181cFA5e |
| TAC | CurveRouter | 0x3F5A41B922a76759b9C77D36b3d337E88cD1dc5e |
Sources: incident and fund tracing2; contract addresses14; forged deposit and custody withdrawal15; tsTON redemption16.
Unable to render diagram.
Root Causes and Defensive Opportunities#
Root cause: Sequencers accepted deposit notifications without verifying that the sending contracts were genuine custody Jetton Wallets for the claimed assets.1
These are recommended mitigations. Their implementation status is unconfirmed.
| Mitigation | Action |
|---|---|
| Wallet authentication | Verify the expected wallet code hash and allowlisted Jetton Master for the asset. Check that the actual message sender matches the custody-wallet address derived from that master and JettonProxy.111 |
| On-chain sender validation | At JettonProxy, reject notification senders that do not match authenticated custody-wallet mappings. This checks the sender before sequencer processing.17 |
| Validation before consensus | Test counterfeit wallets with valid-looking payloads and false master claims. Require rejection before voting; quorum cannot correct a validation error shared by the sequencers.1112 |
| Backing reconciliation | Independently reconcile each asset’s TON custody balance with its TAC representation supply, accounting for pending deposits and withdrawals.1 |
| Rate limits and automatic pauses | Limit each asset’s mint and withdrawal volumes over time. Pause on unexplained backing deficits or excessive activity. TAC reported immediate detection, but the subsequent suspension did not stop the attacker from extracting funds.1 |
| Ongoing review | Review TON validation guidance regularly and rerun attack tests. Obtain independent audits and have TON experts review changes.1 |
Pre-Exploit Testing#
Public documentation. By November 18, 2025, TON’s public documentation warned about fake Jetton wallets and instructed receivers to check notification senders against wallets derived from trusted Jetton Masters. The general attack pattern was therefore public before the incident. This does not show whether the attacker knew TAC was missing the check.18
Testing sequence. These transactions suggest the attacker tested which messages the bridge would accept before attempting larger mints. All times are UTC; dates are in 2026.
| Time | Observed activity | Source TX |
|---|---|---|
| May 10, 22:12 | Initial forged notification used a placeholder destination and incomplete delivery settings. | TON · Mainnet |
| May 10, 22:54 | A legitimate 2 TON bridge transaction contained working message values that may have served as a template for later tests. | TON · Mainnet |
| May 10, 23:21 | Attacker deployed the receiving contract on TAC’s SPB testnet. | TAC · SPB Testnet |
| May 10, 23:33 | The same attacker address deployed the receiving contract on mainnet with identical creation bytecode. | TAC · Mainnet |
| May 10, 23:34 | Sequencers approved the forged message, but the final application call failed. | TAC · Mainnet |
| May 11, 01:36 | A small test minted 0.000001 USD₮ without a genuine deposit, demonstrating that the authenticity check was missing. | TAC · Mainnet |
| May 11, 02:11 | First large BLUM mint, approximately 35 minutes after the successful small test mint. | TAC · Mainnet |
It remains unknown whether the attacker had private information, including information from insiders.
References#
Footnotes#
-
TAC — Post-Mortem Report: TAC Bridge, May 20, 2026. ↩ ↩2 ↩3 ↩4 ↩5 ↩6 ↩7
-
TAC — Appendix II: Onchain Tracing, May 20, 2026. Token amounts, failed withdrawals, swaps, and onward bridging. ↩ ↩2 ↩3
-
TAC — Public recovery offer: 10% bounty and no legal action upon return, May 14, 2026. ↩
-
May 14, 2026 refund transactions — 58M BLUM on TON; 864,702.59 DAI, 5.50877119 WBTC, and 3.09 ETH on Ethereum. The private-key handover is reported in Appendix II; the transactions establish asset transfers. ↩
-
TON documentation — Introduction. ↩
-
TAC documentation — What is TAC? and TON Adapter. ↩
-
Blum — BLUM networks, bridging route, and official contract addresses. ↩
-
Tonstakers — What is tsTON? and Official links and contract addresses. ↩
-
TAC documentation — Asset bridging. ↩
-
TON Enhancement Proposals — TEP-74: Fungible tokens (Jettons) standard. ↩
-
TON documentation — Jetton processing and wallet validation. ↩ ↩2 ↩3
-
TAC documentation — Transaction lifecycle. ↩ ↩2
-
TAC Explorer, verified implementations — Consensus: voting, root validity, and ConsensusReached; CrossChainLayer: proof verification, minting, and burning. ↩
-
TAC documentation — Core contract addresses and Token list. Token issuer addresses are also listed in the issuer sources above. ↩
-
Tonviewer — Forged transfer notification (Step 2) and Genuine USD₮ withdrawal from custody. ↩
-
Tonviewer — 8,277 tsTON unstaking request, May 11, 2026; 9,170.940553938 TON payout to the attacker, May 12, 2026. ↩
-
TON documentation — On-chain Jetton processing: authenticating notification senders. ↩
-
TON documentation — Pre-incident warning about fake Jetton wallets and master-wallet verification, November 18, 2025. ↩